LINUX INFRASTRUCTURE SOFTWARE // ACTIVE PLATFORM

The Unified Control Plane for Your Linux Servers & Containers.

Real-time host telemetry, Docker & Podman container governance, and systemd service supervision in one unified dashboard—with under 20MB RAM overhead and zero open inbound ports.

Agentless SSH or Binary•Ubuntu, Debian, RHEL, Rocky, Arch
x86_64 & ARM64
Overhead
<20MB RAM
Low-overhead compiled binary
Runtimes
Docker & Podman
Socket-level daemon discovery
Network
Outbound TLS
Zero open inbound ports needed
Services
Systemd Control
Unit states, journals & timers
Fleet Compatibility
✓Ubuntu 24.04 / 22.04
✓Debian 12 / 11
✓RHEL 9 / 8
✓Rocky & AlmaLinux
✓Arch Linux
✓x86_64 & ARM64
✓AWS EC2 & Graviton
✓Hetzner Cloud
✓DigitalOcean Droplets
✓Bare Metal & Proxmox
WHY NIRIKSH

Tangible operational outcomes for engineering teams.

Built for DevOps engineers, systems administrators, and engineering leaders who need reliable visibility and control across Linux environments without operational overhead.

FLEET VISIBILITY

Centralized Linux Server Visibility

Eliminate scattered terminal windows, ad-hoc monitoring scripts, and infrastructure blind spots with a single, real-time overview across all your cloud VMs and bare metal hosts.

INCIDENT RESPONSE

Streamlined Infrastructure Operations

Supervise container runtimes, inspect daemon sockets, and manage systemd unit states from one dashboard—minimizing cognitive overhead and shortening triage time during production incidents.

HARDENED SECURITY

Security-Conscious Architecture

Shield your servers behind closed inbound firewalls with outbound-only TLS connections, direct kernel virtual filesystem interfaces, and 100% data sovereignty on your own infrastructure.

FLEXIBLE ADOPTION

Scalable Plans for Any Stage

Start with a lightweight, self-hosted Community Edition on a single box, and expand effortlessly into centralized multi-cloud fleet management and air-gapped enterprise environments as needs grow.

PLATFORM SHOWCASE // UNIFIED COCKPIT

Granular server oversight, auditing, and control in one console.

Inspect host telemetry, audit SSH configurations against hardening benchmarks, identify disk space hogs, and execute authorized remediation actions directly from a single unified cockpit with zero open inbound ports.
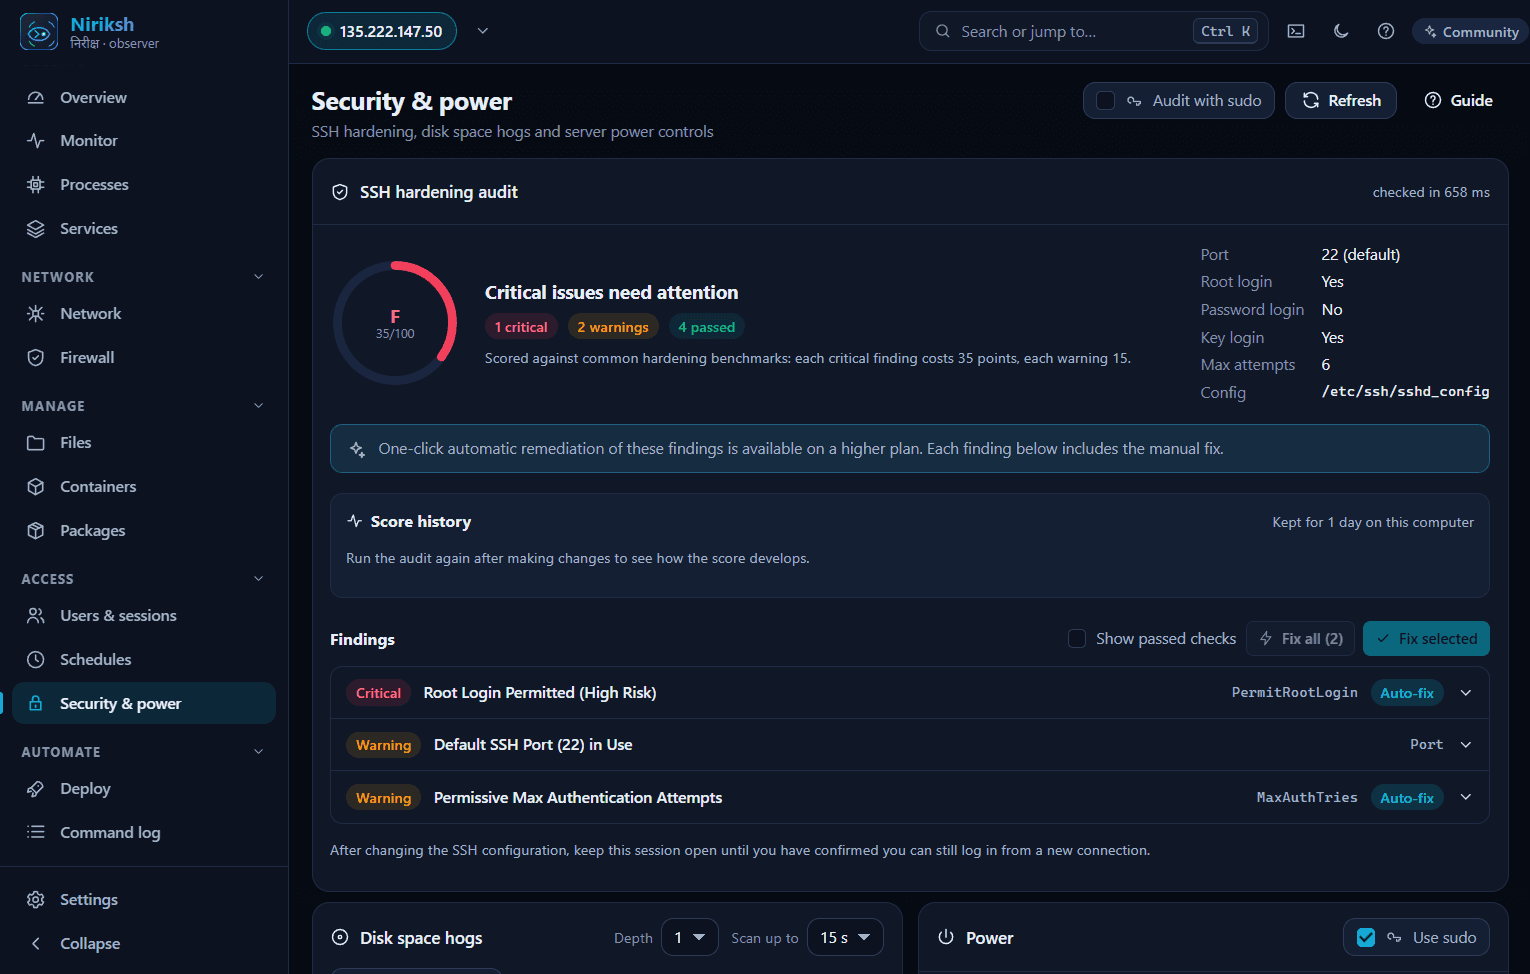
niriksh // live-cockpit // security & power
Live Host
NIRIKSH Linux & Container Control Plane Dashboard showing SSH hardening audit, disk space hogs, and server governance
SECURITY & ARCHITECTURE

Engineered for strict security and minimal host footprint.

Technical architecture specifications covering network boundaries, direct Linux kernel interfaces, memory overhead, and private VPC data containment.

01 // RUNTIME ARCHITECTURE

Host Runtime Footprint

Low-overhead compiled binary operating with zero external interpreter dependencies.

Memory Overhead:<20MB resident set size (RSS) with imperceptible CPU consumption (<0.1%).
Zero Dependencies:Single static binary; no Python, JVM, Node, or dynamic library dependencies required.
PSI Aware:Monitors Linux Pressure Stall Information to prevent host resource contention.
Lifecycle Supervision:Native systemd service integration with automatic restart and crash supervision.
02 // NETWORK BOUNDARY

Transport Security & Firewalls

Outbound-only encrypted tunnels ensuring zero public inbound port exposure.

Inbound Firewall:Zero open listening ports required; SSH Port 22 and internal ports remain shielded.
Cryptographic Identity:Mutual TLS (mTLS 1.3) encryption with token-authenticated agent node identity.
Outbound Reverse Tunnel:Persistent outbound WebSocket connection initiating from the agent to the control center.
Connection Resilience:Automatic heartbeat keepalive with deterministic exponential reconnect backoff.
03 // KERNEL INTERFACES

Kernel Interfaces & Privilege Scoping

Direct D-Bus and virtual filesystem sampling operating on the principle of least privilege.

Direct Kernel APIs:Native sampling via /proc/loadavg, /proc/meminfo, and statvfs without shell parsing.
D-Bus IPC Control:Direct Linux D-Bus communication for instant systemd unit supervision and journal queries.
Daemon Sockets:Local UNIX domain socket auditing for Docker (/var/run/docker.sock) and Podman engines.
Least Privilege:Unprivileged read-only telemetry by default; sudo is scoped strictly to active commands.
04 // DATA SOVEREIGNTY

Data Sovereignty & Containment

Complete telemetry, credential, and log isolation inside your private infrastructure.

Zero External Egress:Server metrics, container metadata, and session logs never leave your designated control plane.
Air-Gapped Capable:Operates fully offline within isolated private subnets, air-gapped clusters, and VPCs.
Self-Hosted Infrastructure:Deployable on customer-owned bare-metal servers or private cloud virtual machines.
Local Metric Retention:Telemetry history and audit trails are stored strictly in customer-controlled storage volumes.
PLANS & PRICING (USD)

Transparent pricing for fleets of any scale.

Choose the right plan for your infrastructure—from a forever free self-hosted box to multi-cloud production fleets and air-gapped enterprise environments.

FREE FOREVER

Community

Individual engineers & homelabs

$0Free forever

Self-hosted single node monitoring with full CPU, RAM, and container telemetry with zero cloud dependencies.

INCLUDED
1 host node (self-hosted compiled binary)
Real-time CPU, RAM, swap & disk telemetry
Docker & Podman daemon auto-discovery
Systemd unit state & journal inspection
Interactive human account (UID ≥ 1000) auditing
Zero inbound open firewall ports required
Community forum support
INDIVIDUAL PRO50% OFF

Professional

Independent developers & production VPS

$4.99$9.99/ month

Enhanced telemetry with historical retention, web SSH terminal access, and proactive threshold alerts.

INCLUDED
Up to 3 server nodes included
7-day historical telemetry retention
Web-based SSH terminal with session logs
Email & Webhook threshold alerts
Docker container restarts & volume auditing
Systemd timers & crontab countdown tracking
Standard email support
RECOMMENDED
MOST POPULAR40% OFF

Team

Engineering teams & cloud fleets

$14.99$24.99/ month

Centralized multi-cloud fleet governance across AWS, Hetzner, DO, and bare metal with team alerting.

INCLUDED
Up to 25 server nodes included
Centralized multi-provider fleet dashboard
30-day historical telemetry retention
Proactive Slack, Discord & Webhook alerts
Consolidated crontab & systemd fleet scheduler
1-Click production stack deployer (Compose)
Priority technical support
FLEET SCALE28% OFF

Enterprise

High-scale production fleets & companies

$49.99$69.99/ month

Comprehensive fleet oversight with extended data retention, team RBAC, and dedicated technical support.

INCLUDED
Up to 100 server nodes included
1-year telemetry retention & log export pipelines
Team Role-Based Access Control (RBAC)
Audited multi-user SSH terminal with session records
Automated host hardening & privilege checks
Dedicated technical support & 99.9% SLA
AIR-GAPPED & VPC

Custom Enterprise

Regulated industries, banks & private VPCs

CustomContact Sales

Dedicated control plane deployed inside your own private VPC or air-gapped data center with strict sovereignty.

INCLUDED
Unlimited Linux host, VM & container nodes
100% air-gapped on-premises or private VPC deployment
SSO with SAML 2.0 / OIDC identity federation
Custom metric retention & immutable audit logs
Architecture walkthrough & migration review
Assigned Senior Solution Engineer & 99.99% SLA
TECHNICAL QUESTIONS

Frequently Asked Questions

Practical answers to common architecture, security, and deployment questions from Linux systems engineers and technical leads.

Whether connecting agentlessly over SSH or via the lightweight compiled binary, passive telemetry (CPU, RAM, swap, and disk mount status) only requires standard unprivileged read access to /proc and /sys. To audit container runtimes, it connects to the local Docker or Podman daemon socket. Sudo capabilities are only utilized when explicitly executing active administrative actions, such as restarting systemd units, running CIS compliance remediation, or executing stack deployments.

No. The NIRIKSH agent operates via authenticated, outbound-only TLS connections back to the central control plane. You can keep all inbound firewall ports (including SSH Port 22) completely shielded from the public internet. It works seamlessly behind corporate NATs, strict AWS Security Groups, and private subnets.

Yes. NIRIKSH is designed with complete data sovereignty in mind. Both the central control plane and the host agents can be deployed entirely inside your own private VPC, on-premises bare-metal cluster, or offline air-gapped network with zero external internet dependencies or telemetry reporting to outside servers.

Cockpit is built primarily for single-server administration and lacks unified multi-cloud fleet grouping. Portainer is strictly tailored for container orchestration (Docker/K8s) and does not provide host-level systemd daemon management, scheduled crontab oversight, or Linux user session auditing. NIRIKSH unifies host OS telemetry, systemd daemons, user security, and Docker/Podman engines into a single cohesive control plane.

NIRIKSH supports modern Linux distributions including Ubuntu 20.04/22.04/24.04 LTS, Debian 11/12, RHEL 8/9, Rocky Linux, AlmaLinux, Arch Linux, and Amazon Linux 2023. It runs natively across both x86_64 (AMD64) and aarch64 (ARM64, including AWS Graviton and Ampere instances).

When utilizing agentless SSH mode, local host resident memory overhead is zero (probes execute on demand). When running the optional compiled binary agent for continuous sub-second telemetry streaming, it consumes less than 20MB of resident RAM and under 0.1% CPU compute overhead, keeping your server compute dedicated to your production workloads.
GET STARTED WITH NIRIKSH

Ready to simplify your Linux server operations?

Deploy NIRIKSH across your Linux fleet in under two minutes, or schedule an architecture walkthrough with our engineering team to discuss custom multi-cloud or air-gapped requirements.

Schedule Technical Walkthrough
Zero Open Inbound Ports•100% Data Sovereignty•<20MB RAM Host Footprint